The Pirate Post ha ricondiviso questo.

The media in this post is not displayed to visitors. To view it, please go to the original post.

The media in this post is not displayed to visitors. To view it, please go to the original post.

✨ Flying Eagle: il RAT Android che spiava per conto della «polizia cinese» finisce nelle mani sbagliate
#CyberSecurity
insicurezzadigitale.com/flying…

@informatica


Flying Eagle: il RAT Android che spiava per conto della «polizia cinese» finisce nelle mani sbagliate


Un archivio da 388 MB chiamato semplicemente “中国龙.zip” (Chinese Dragon) circola da mesi sui canali Telegram del cybercrime cinese. Dentro c’è il codice sorgente completo di Flying Eagle, un framework criminale che non è “solo” un trojan Android, ma una vera piattaforma industriale per costruire e gestire spyware mobile su larga scala — la stessa che ha alimentato una finta app della “polizia cinese” usata per svuotare conti Alipay e WeChat. Ora che il codice è trapelato, i ricercatori di Hunt.io e dell’analista indipendente NetAskari hanno mappato 170 server ancora attivi legati all’infrastruttura, mentre tra gli stessi criminali è scoppiato un regolamento di conti che ha già partorito un erede, Night Dragon.

Una app “governativa” che rubava le password


La storia riemerge alla luce del sole a giugno 2026, quando il National Cybersecurity Notification Center cinese ha diffuso un avviso pubblico su una applicazione fraudolenta che si spacciava per “公安一网通办”, un servizio online delle Pubbliche Sicurezze Provinciali (GongAn). L’app veniva distribuita dal dominio 110gongan[.]com e, una volta installata, era in grado di rubare dati di pagamento e prendere il controllo remoto del dispositivo. Le autorità hanno raccomandato a chi l’avesse installata di rimuoverla, scansionare il device, cambiare le password degli account coinvolti, congelare i canali di pagamento in caso di movimenti sospetti e sporgere denuncia.

Quell’app era solo la punta dell’iceberg. Dietro c’era Flying Eagle: un builder che permette a un operatore di scegliere nome, icona e testo di adescamento dell’app, indicare l’indirizzo C2, e generare in automatico un APK Android firmato e pronto alla distribuzione, partendo da due template base. I campioni prodotti dal builder vengono rilevati dai motori antivirus come SpyNote, famiglia di RAT Android nota da anni, e sfruttano i servizi di accessibilità di Android per l’escalation di privilegi e l’iniezione di gesture — controllo pressoché totale del dispositivo della vittima.

Non un malware, una piattaforma industriale


Ciò che rende Flying Eagle diverso da un comune RAT è la sua natura di prodotto “chiavi in mano” per operatori criminali con competenze tecniche limitate. L’archivio trapelato contiene un intero deployment Docker con server nginx, PHP, MySQL e un WebSocket server Node.js, oltre a toolchain complete per la compilazione Android (Java 11 e Android SDK build tools), template di phishing pronti — servizi di streaming per adulti in cinese, cloni di TikTok, applicazioni finanziarie e persino landing page per finti progetti di pubblica utilità che rimandano all’operatore statistiche di visite e download — e un certificato TLS di default.

Gli URL di callback verso il server di comando e controllo, incorporati in ogni APK generato, sono cifrati con AES-128-CBC usando IV, password e salt hardcoded, con chiave derivata tramite PBKDF2-SHA1 a 65.536 iterazioni. I commenti nel codice sorgente rivelano che questi parametri servono a mantenere la compatibilità con il binario Windows .NET originale (EaodWorker.exe), confermando che la versione Docker trapelata è una porting diretto di uno strumento più vecchio. Per abbassare l’entropia del pacchetto ed eludere l’analisi statica, il builder inietta inoltre tra 2,8 e 3,5 MB di JSON Base64 travestito da cache di configurazione SDK legittima.

La caccia ai 170 server


Per ricostruire l’estensione reale dell’infrastruttura, i ricercatori hanno sfruttato un’impronta digitale ricorrente: i server Flying Eagle rispondono con un redirect HTTP 302 verso l’endpoint HTTPS, includono l’header Strict-Transport-Security: max-age=31536000 e, prima che carichi il branding personalizzato dell’operatore, mostrano brevemente il titolo di pagina “AdminPro”. Incrociando questa firma con il certificato TLS di default incluso nell’archivio trapelato, sono stati identificati 158 server tramite il titolo della pagina e altri 12 tramite il certificato, per un totale di 170 server attivi negli ultimi 30 giorni di telemetria — una cifra che i ricercatori stessi definiscono conservativa, perché esclude i server che non restituiscono esattamente il redirect atteso. È importante sottolineare che questo numero descrive impronte infrastrutturali, non necessariamente vittime, operatori o C2 confermati uno per uno.

Buona parte dell’infrastruttura, inclusi i due IP citati nell’avviso ufficiale cinese (207.56.30.188 e 207.56.30.194), è ospitata su AS54801 (Zillion Network Inc.), un provider di Hong Kong che compare più volte come piattaforma preferita per il malware mobile in questo ecosistema. Uno dei server ha addirittura mostrato, temporaneamente, un pannello di gestione dispositivi che indicava utenze “guadagna facile” tipiche di operatori criminali a scopo di lucro.

Ladri tra ladri: quando i criminali si smascherano a vicenda


Il canale Telegram Yx科技 (Yx Technology), creato ad aprile 2026, non ha esordito con un semplice annuncio: i primi messaggi erano istruzioni passo passo su come usare strumenti di accesso remoto per svuotare conti Alipay e WeChat Pay, con le vittime definite spregiativamente “pesci” (鱼) e servizi di cash-out offerti al 20-50% della transazione. Il 26 aprile il canale ha distribuito gratuitamente il pacchetto Flying Eagle sotto forma dell’archivio Chinese Dragon.

Da qui la parte più “da romanzo”: un secondo canale, SQLRCE0, ha iniziato a far girare messaggi secondo cui un attore non identificato avrebbe compromesso l’infrastruttura clienti di Yx Technology, sottraendo dati relativi a 189 server Flying Eagle. La rivendicazione non è stata confermata in modo indipendente dai ricercatori, ma il caos generato — codice rubato che diventa a sua volta merce rubata — è di per sé indicativo della frammentazione e della sfiducia reciproca dentro questi ecosistemi criminali cinesi.

Night Dragon: l’erede è già online


Il 23 giugno 2026 lo stesso canale SQLRCE0 ha lanciato Night Dragon, un nuovo kit di controllo Android indipendente. I ricercatori hanno individuato al momento solo due server associati, entrambi ospitati — non a caso — sullo stesso provider hongkonghese AS54801. Uno dei pannelli esposti mostrava 46 dispositivi “online” e 29 “attivi”, tutti geolocalizzati in Cina, ma non è stato possibile stabilire se si tratti di vittime reali o di dati di test. Una seconda versione del framework risultava già in sviluppo al 12 luglio. È bene chiarire un possibile equivoco: questo Night Dragon del 2026 non ha nulla a che vedere con l’omonima campagna di spionaggio cinese documentata da McAfee nel 2011 — qui si parla di crimeware finanziario, non di intelligence offensiva.

Due righe per i difensori


  • Diffidare sistematicamente di APK “governativi” o “di pubblica utilità” distribuiti fuori dal Play Store: il sideloading resta il principale vettore di infezione per questa famiglia di minacce.
  • Monitorare le richieste di attivazione dei servizi di accessibilità Android da parte di app non aziendali: è il meccanismo chiave usato per l’escalation di privilegi e il controllo remoto.
  • Per i team threat intelligence, il fingerprint “AdminPro” + redirect 302 + certificato di default è riutilizzabile per identificare infrastrutture derivate dallo stesso codice trapelato, comprese eventuali nuove fork oltre a Night Dragon.
  • Il caso dimostra ancora una volta come i leak di codice sorgente criminale — volontari o meno — accelerino la proliferazione di varianti, più che ridurre la minaccia: ogni fork riparte da una base già matura.


Indicatori di compromissione

# Domini/infrastruttura Flying Eagle
110gongan[.]com          # App fasulla "polizia cinese" (GongAn)
fusu.us[.]ci
fusu666[.]cc              -> 207.56.30[.]188
ls.j2x8a[.]top             -> 207.56.30[.]194 (cert emesso 2026-06-04)
xyttkx[.]cc, txl.xyttkx[.]cc, h5.xyttkx[.]cc, alcs.xyttkx[.]cc
# IP
207.56.30[.]188   AS54801 Zillion Network Inc. (Hong Kong)
207.56.30[.]194   AS54801 Zillion Network Inc. (Hong Kong)
# Archivio trapelato
中国龙.zip (Chinese Dragon) - 388 MB, distribuito via Telegram (Yx科技) dal 2026-04-26
# Campioni APK (SHA256)
c692ad120cc90548d48dbe57d006f2403c49833b8993af3c38fe031eb39999bd  autoclicker_pro.apk
4395db6ad53a415532673b16f5b64207d53cecc5b15a736c038cf3890368a164  net.extractor.terminator.channel.apk
5dee5cde6f2874c582effe302960b21569ee007e9e0cd4f7499d418cceb9095b  com.sequencer.classifier.processor.apk
b803cd5032dc1abd7aabc45c8cadc471c8a59872a95d48807f13e230c58230f3  net.cataloger.curator.stager.apk
d8a82d7b4457352774772bfac094127d7f67526ae7011d838cc3f7ccc15fd86e  net.listener.transactor.authorizer.apk
# Fingerprint di caccia
HTML title = "AdminPro", redirect HTTP 302 -> HTTPS,
header Strict-Transport-Security: max-age=31536000
# Night Dragon (lancio: 2026-06-23, stesso hosting AS54801)

Fonti primarie: Hunt.io/NetAskari, “Flying Eagle Android RAT: Leaked Source Code, 170 Active Servers, and a New Platform Called Night Dragon” (28 luglio 2026); The Hacker News, 29 luglio 2026; avviso pubblico del National Cybersecurity Notification Center cinese (18 giugno 2026).

The Pirate Post ha ricondiviso questo.

The media in this post is not displayed to visitors. To view it, please go to the original post.

The media in this post is not displayed to visitors. To view it, please go to the original post.

✨ Un attacco informatico spegne 21 milioni di angolani alla vigilia della più grande IPO del paese: cosa sappiamo su Unitel
#CyberSecurity
insicurezzadigitale.com/un-att…

@informatica


Un attacco informatico spegne 21 milioni di angolani alla vigilia della più grande IPO del paese: cosa sappiamo su Unitel


Alle 2:20 del mattino di martedì 28 luglio, poche ore prima che le azioni di Unitel iniziassero a essere scambiate sulla borsa di Luanda nella più grande IPO della storia angolana, i sistemi core del principale operatore di telecomunicazioni del paese sono andati in tilt. Voce, dati mobili e connettività internet si sono fermati per oltre 21 milioni di persone, quasi metà della popolazione dell’Angola. La tempistica, quasi chirurgica, ha subito sollevato una domanda che l’azienda stessa non ha escluso: è stato un sabotaggio pensato per far deragliare la quotazione?

Un blackout nazionale nelle 24 ore che contavano di più


Unitel, ex monopolista statale passato sotto controllo pubblico nel 2022 dopo il sequestro delle quote un tempo detenute da Isabel dos Santos, figlia dell’ex presidente José Eduardo dos Santos, ha dichiarato di aver rilevato l’incidente attorno alle 2:20 locali del 28 luglio e di aver attivato “immediatamente” i protocolli di risposta e contenimento. Il ripristino graduale dei servizi mobili è iniziato solo alle 11:45 del giorno successivo, provincia per provincia, con gli SMS rimasti fuori uso più a lungo di voce e dati. Le infrastrutture fisse su fibra e wireless, che servono istituzioni pubbliche e aziende, sono invece rimaste operative per tutta la durata dell’incidente, un dettaglio che suggerisce un impatto concentrato sui sistemi core mobili piuttosto che su un evento di disponibilità generalizzato.

Il dato più interessante arriva dalla telemetria di rete, non dai comunicati aziendali. Recorded Future News ha verificato che i prefissi IP di Unitel sono rimasti annunciati su internet per tutta la durata dell’incidente: i router che connettono l’operatore al resto della rete globale non sono mai andati offline, come invece accadrebbe in un classico taglio di connettività a monte o in un attacco DDoS volumetrico. Il traffico misurato da Cloudflare Radar mostra invece un crollo netto proprio nella finestra dell’attacco, confinato esclusivamente a Unitel mentre gli altri operatori angolani non hanno mostrato alcun degrado. La lettura più plausibile è quella di un incidente che ha disabilitato sistemi interni critici — probabilmente elementi core della rete mobile o piattaforme di autenticazione/billing — piuttosto che un attacco alla connettività esterna.

Il contesto: una IPO da record e un sospetto legittimo


L’attacco è arrivato meno di 24 ore prima del debutto di Unitel alla BODIVA, la borsa angolana, nell’ambito del programma di privatizzazioni del presidente João Lourenço volto a ridurre il peso dello stato nell’economia post-marxista del paese. L’offerta, gestita dall’istituto statale di gestione patrimoniale IGAPE per una quota del 15%, è stata sottoscritta oltre il 120%, con più di 11.000 investitori coinvolti: un test di appetito del mercato per gli asset statali angolani, considerato un possibile precursore per la futura quotazione della compagnia petrolifera nazionale Sonangol. Nonostante il blackout in corso, la negoziazione è comunque partita mercoledì, valutando la società 2,14 miliardi di dollari e raccogliendo circa 321 milioni per le casse pubbliche.

Unitel stessa ha dichiarato di non poter escludere che l’attacco fosse “deliberato e mirato”, proprio a causa della coincidenza con l’avvio delle negoziazioni azionarie. Nessun gruppo ha rivendicato la responsabilità, e non ci sono conferme pubbliche su esfiltrazione di dati o impiego di ransomware. Un elemento di contesto rilevante: settimane prima dell’incidente, il collettivo “CyberTeam” — coinvolto in un attacco contro l’Assemblea Nazionale angolana — aveva lasciato intendere che Unitel potesse essere il bersaglio successivo, sebbene al momento non vi sia alcuna prova che leghi quel gruppo all’incidente di luglio. L’interruzione ha avuto ricadute anche sull’economia reale: i terminali POS collegati alla rete Unitel hanno smesso di funzionare, colpendo pagamenti digitali e comunicazioni aziendali in un paese dove la penetrazione mobile è lo scheletro portante dei servizi finanziari.

Perché conta per chi guarda alla sicurezza delle telco


Al di là del singolo episodio, l’incidente Unitel è un caso di scuola su tre fronti che meritano attenzione da parte di chi si occupa di protezione delle infrastrutture critiche. Primo: la tempistica di un attacco può essere un’arma quanto il payload stesso. Colpire un operatore telco nelle ore immediatamente precedenti un evento finanziario ad alta visibilità massimizza il danno reputazionale e la pressione su chi deve decidere se procedere comunque con l’IPO, indipendentemente dalla natura tecnica dell’attacco. Secondo: la persistenza dei prefissi BGP durante l’intero blackout conferma ancora una volta che gli attacchi più dannosi contro le telco moderne non colpiscono più solo la disponibilità della rete di trasporto, ma i sistemi applicativi core — HLR/HSS, piattaforme di autenticazione, sistemi di billing — la cui compromissione può paralizzare i servizi senza mai far sparire l’infrastruttura di routing dai radar esterni. Terzo: la sequenza di ripristino, provincia per provincia e canale per canale (voce e dati prima, SMS dopo), suggerisce un lavoro di remediation selettivo su sistemi distinti piuttosto che un semplice riavvio, coerente con un incidente di sicurezza più che con un guasto tecnico diffuso.

Per i team di difesa delle telco, specialmente in mercati emergenti dove eventi di mercato ad alta visibilità (IPO, fusioni, aste di spettro) sono sempre più frequenti, il caso Unitel rafforza la necessità di considerare tali finestre temporali come periodi a rischio elevato, con controlli rafforzati su change management, accessi privilegiati ai sistemi core e monitoraggio della telemetria BGP/traffico in tempo reale per distinguere rapidamente un attacco interno da un problema di connettività esterna. Vale la pena notare che nessuna autorità di regolamentazione, né la BODIVA né l’authority dei mercati di capitale angolana, ha rilasciato dichiarazioni pubbliche sull’accaduto: un silenzio istituzionale che lascia molte domande aperte su attribuzione, impatto reale sui dati dei clienti ed eventuali richieste estorsive dietro le quinte.

Cosa manca ancora al quadro


A oggi restano senza risposta le domande più rilevanti per una piena classificazione dell’incidente: quale vettore di accesso iniziale è stato usato, se ci sia stata esfiltrazione di dati dei 21 milioni di abbonati, e se dietro l’attacco ci sia un gruppo con motivazioni finanziarie, un attore hacktivista legato a tensioni politiche interne, oppure un operatore state-sponsored interessato a colpire la privatizzazione degli asset angolani. La vicenda merita un monitoraggio attento nelle prossime settimane, sia per eventuali rivendicazioni su forum underground sia per comunicazioni obbligatorie che Unitel, in quanto società ora quotata, dovrà rendere al mercato.

  • 28 luglio, ore 2:20 locali: rilevamento dell’incidente sui sistemi core Unitel
  • 28-29 luglio: interruzione totale di voce, dati mobili e SMS a livello nazionale; rete fissa non impattata
  • 29 luglio, ore 11:45: avvio del ripristino graduale provincia per provincia
  • 29 luglio: debutto di Unitel alla BODIVA nonostante l’incidente in corso, raccolta di circa 321 milioni di dollari
  • Nessuna rivendicazione pubblica, nessuna conferma di esfiltrazione dati al momento della pubblicazione


The Pirate Post ha ricondiviso questo.

In Sachsen-Anhalt könnte die AfD die Landtagswahl gewinnen. Dem freien Radio @RadioCORAX aus Halle will der rechtsextreme Landesverband die Finanzierung streichen. Was macht das mit den meist ehrenamtlichen Radiomacher:innen? Ein Interview über Medien im Visier von Rechtsextremen.

netzpolitik.org/2026/freier-ra…

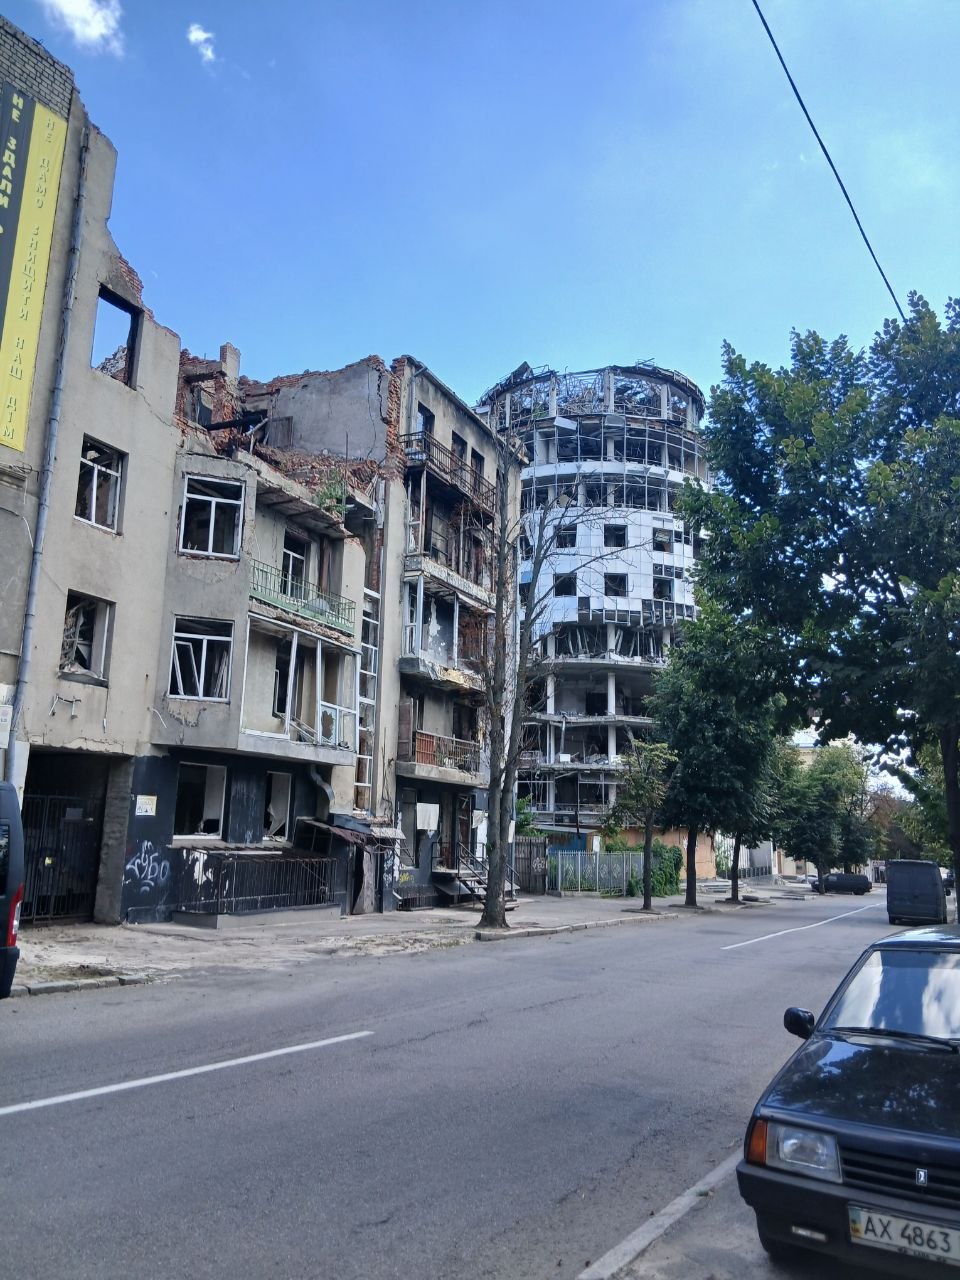
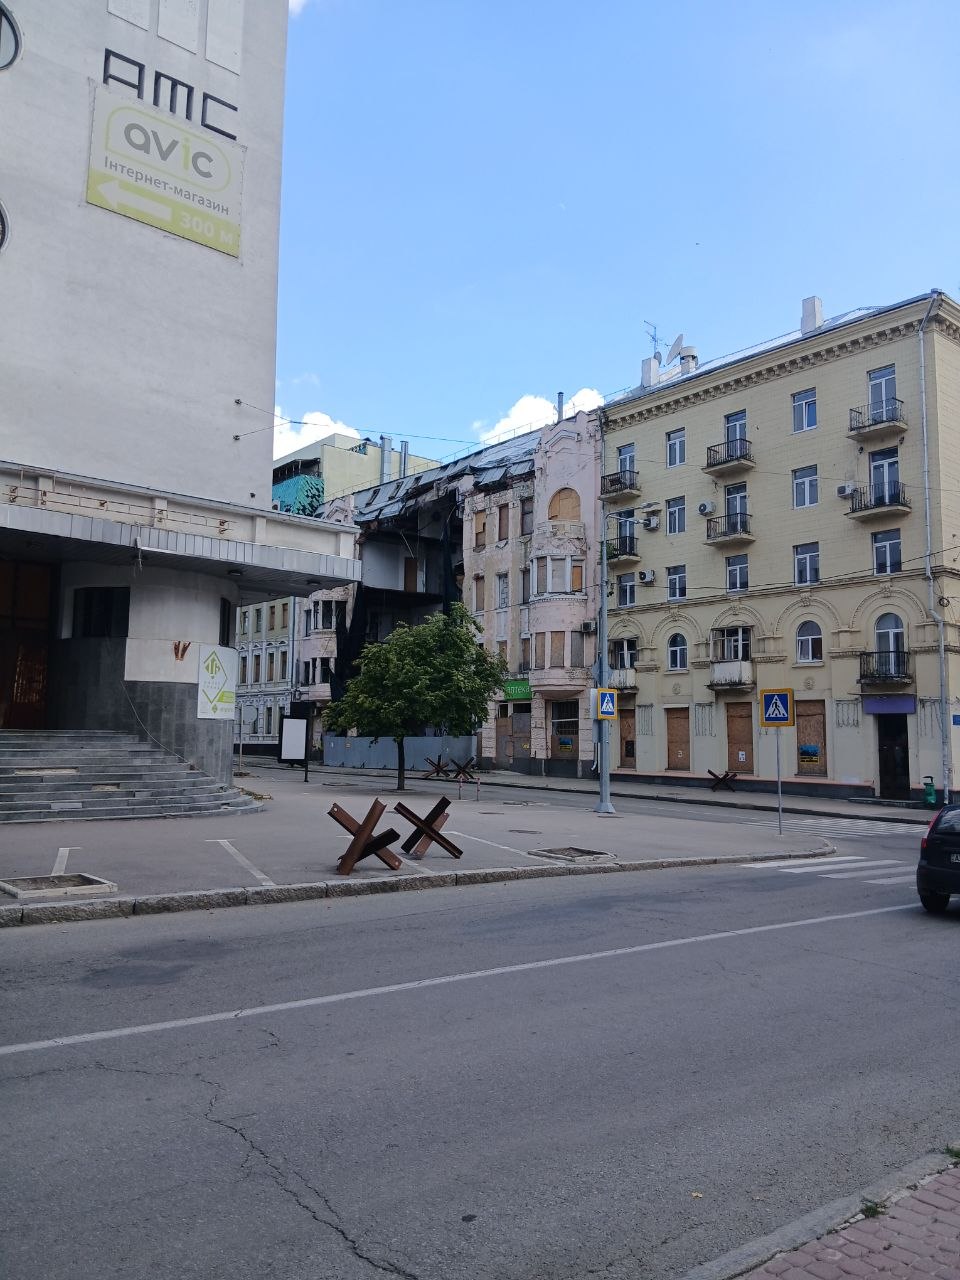
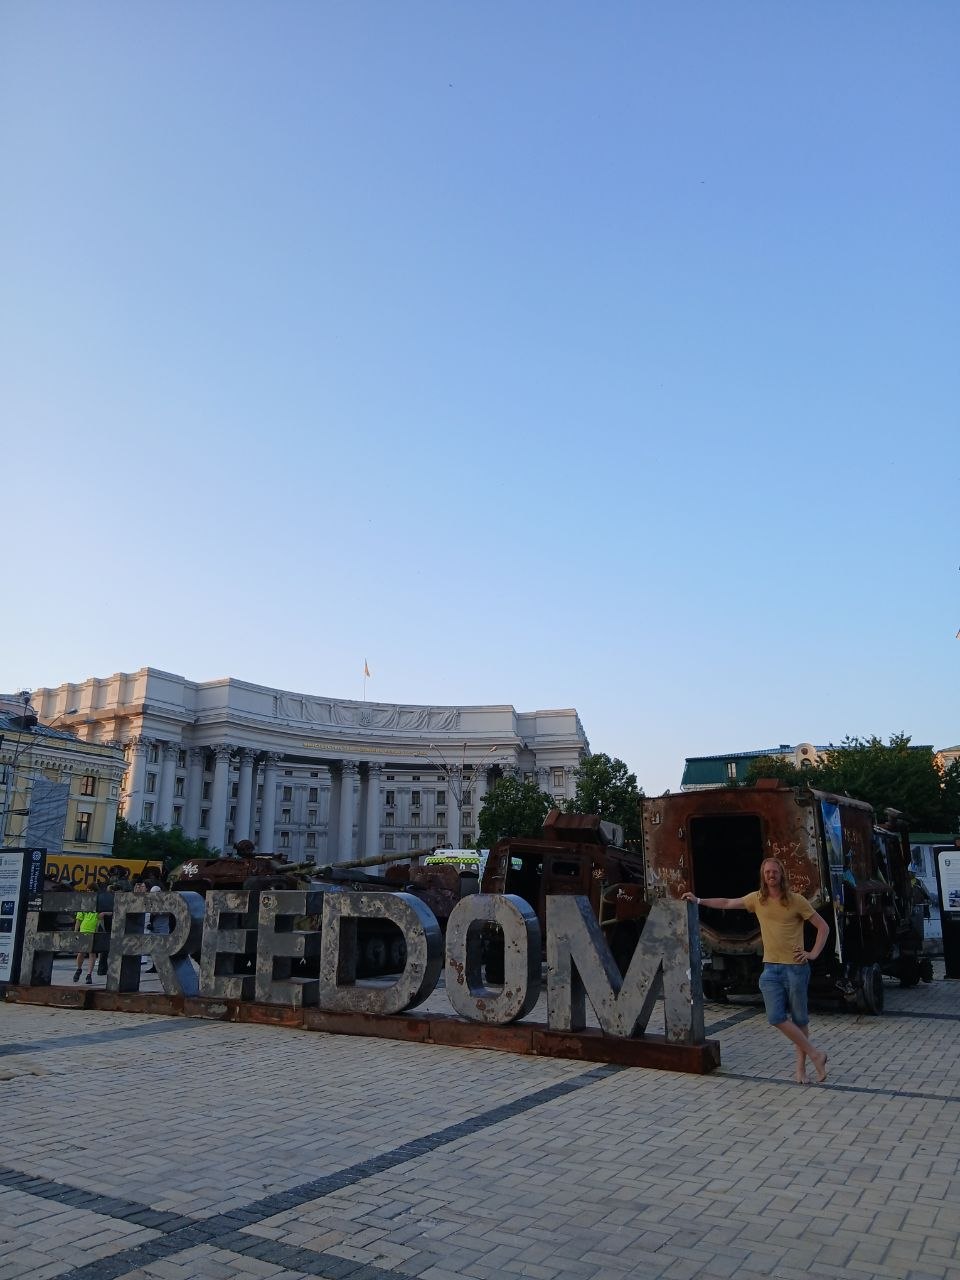
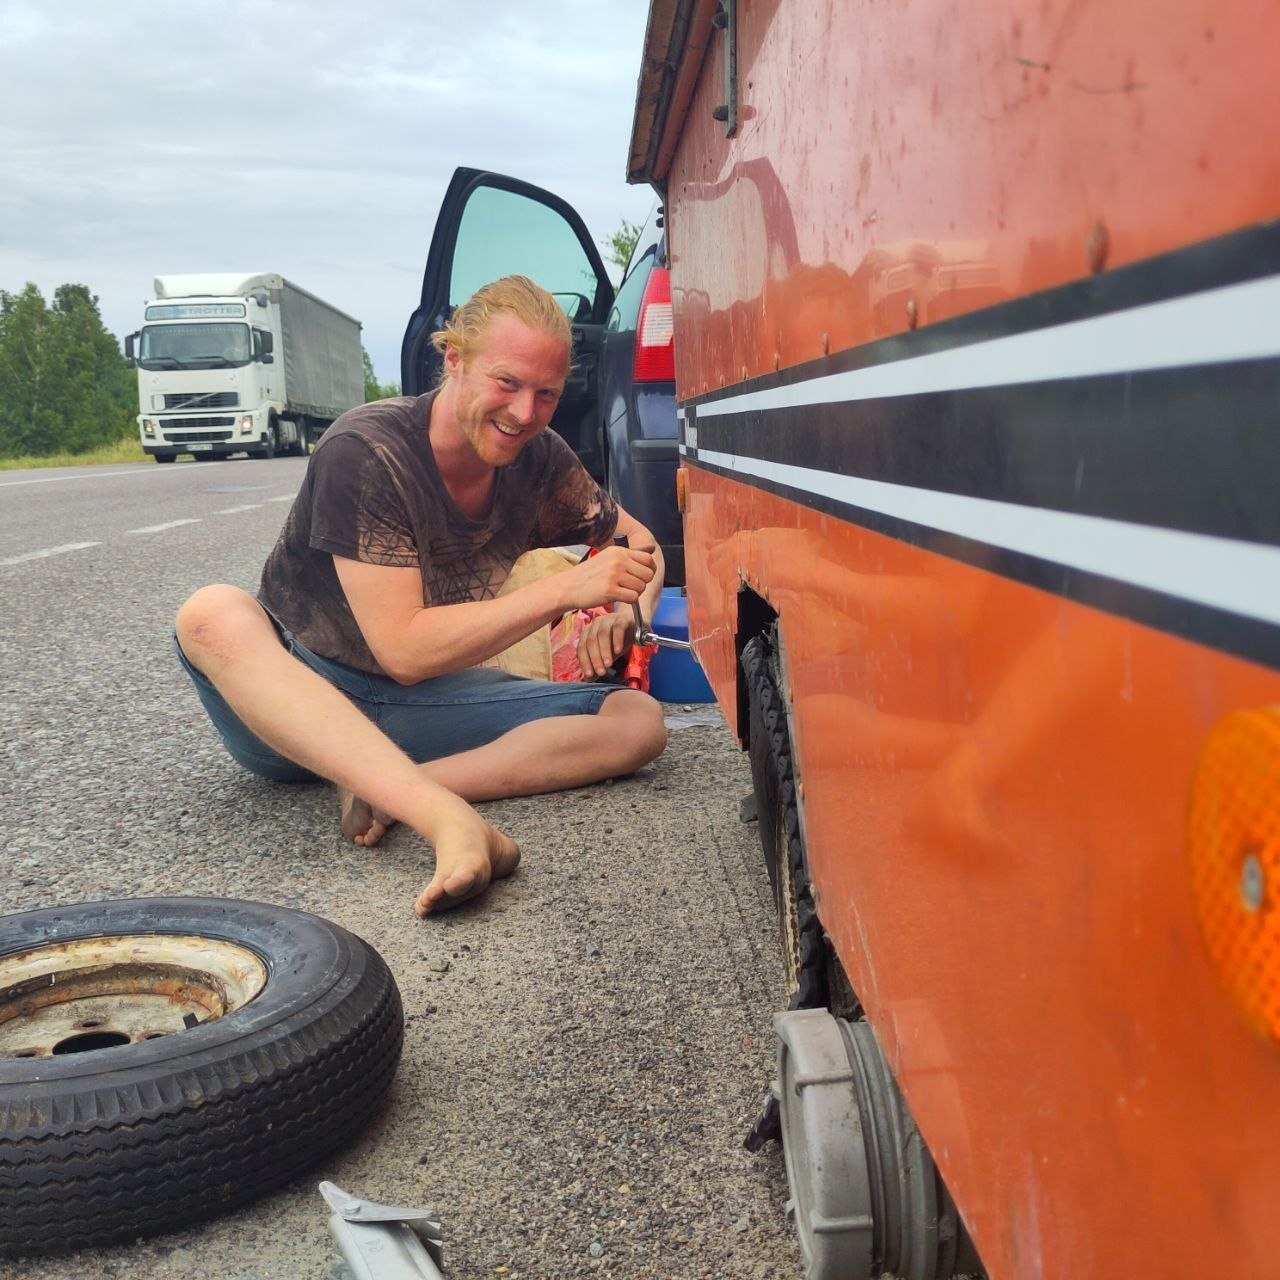
Verslag van mijn reis door Oekraïne


De afgelopen vier jaar ben ik vele malen naar Oekraïne gereisd om humanitaire hulp te leveren. Normaal gesproken verlopen deze reizen vrij eenvoudig: ik rijd rechtstreeks naar een opslaglocatie, laad de goederen uit, breng een dag of twee door met lokale vrijwilligers en keer daarna terug naar huis. Deze reis was anders. Een groep Oekraïense […]

Het bericht Verslag van mijn reis door Oekraïne verscheen eerst op Piratenpartij.

Elezioni e Politica 2026 reshared this.

The Pirate Post ha ricondiviso questo.

☕ CYBERBRIEFING MATTUTINO — Domenica 2 agosto 2026

👉 Leggi tutti gli aggiornamenti delle ultime 24 ore:
ilpuntocyber.rfeed.it/article.…

#newsletter #cybersecurity
@informatica

The Pirate Post ha ricondiviso questo.

The media in this post is not displayed to visitors. To view it, please go to the original post.

BlackTech’s Linux Backdoor Blends In by Routing Through Your Own Proxy Server
#CyberSecurity
securebulletin.com/blacktech-b…
The Pirate Post ha ricondiviso questo.

The media in this post is not displayed to visitors. To view it, please go to the original post.

Keycloak Patches Flaw That Let Restricted Admins Peek at Users Outside Their Scope
#CyberSecurity
securebulletin.com/keycloak-br…
The Pirate Post ha ricondiviso questo.

The media in this post is not displayed to visitors. To view it, please go to the original post.

Fake macOS Update Screens Are Tricking Mac Users Into Handing Over Crypto Wallets
#CyberSecurity
securebulletin.com/north-korea…
The Pirate Post ha ricondiviso questo.

The media in this post is not displayed to visitors. To view it, please go to the original post.

Unauthenticated RCE Flaw in JetBrains TeamCity Puts Software Supply Chains at Risk
#CyberSecurity
securebulletin.com/jetbrains-t…
The Pirate Post ha ricondiviso questo.

CODING FEDIVERSE

Da un po’ di tempo sto lavorando ad un progetto per il #fediverso. L’idea è quella di creare un software che possa permettere la gestione di un social network semplice e pulito con relazioni tra utenti, largo spazio per scrivere e community.

Il punto centrale però è riprendere a sfruttare le capacità server largamente disponibili: PHP+Mysql.
Niente server dedicati e niente requisiti “costosi”. Qualcosa che giri su shared hosting.

Mi piace questo concetto perchè penso che con la semplicità (dando a tutti una possibilità) il fediverso e il web decentralizzato può aumentare la sua diffusione.

Ho quindi creato #Openbook, un nuovo software integrato nel fediverso che gira con PHP+Mysql su hosting comuni.

Ho aperto un repo per iniziare a far vedere il primo timido codice sorgente: github.com/insicd/openbook

Per testarlo ho anche aperto una prima istanza di Openbook qui: openb.app

Il mio account è @nuke@openb.app

La home del progetto: about.openb.app

È ancora embrionale ma se volete farvi un giro…
C’è anche già su @fo qui: fediverse.observer/openb.app

in reply to Ingordi Channel

Non essendo un client alternativo a Mastodon, non si può accedere con account Mastodon esistenti.
Tutto quello che si produce all'interno di Openbook è raggiungibile ovunque nel fediverso, e viceversa... Però se vuoi usare Openbook come software, bisogna loggarsi con un account dentro una istanza openbook, come per esempio openb.app
The Pirate Post ha ricondiviso questo.

Elimina il banner dei cookie per scegliere una volta per tutte che non ne vuoi? Allora contatta i tuoi rappresentanti al Parlamento europeo e chiedi loro di sostenere l'articolo 88b del #GDPR nel documento programmatico digitale!

#KillTheCookieBanner ci ricorda che ripetere la stessa domanda su ogni sito non produce necessariamente un consenso consapevole, ma anzi abitua l’utente a superare il problema nel modo più semplice: pagando con i propri dati.

killthecookiebanner.eu/?page_i…

@privacypride@feddit.it

Report from the Frontlines in Ukraine


The media in this post is not displayed to visitors. To view it, please log in.

The following is a report from PPI Board member and representative from the Pirate Party of the Netherlands, Mark Anthony van Treuren about his observations during humanitarian missions in Ukraine.

Many people wanted to join the army in the beginning to defend their country from the Russians. In the last year corruption from generals has led to unnecessary deaths among the soldiers. Supplies not arriving. Or money disappearing. And choices made that got people killed. There is an unofficial system that allows you to get a safe job if you have the right friends. It has become more difficult to get new soldiers. So people are now being picked up from the street and brought to the frontline. If you have friends in the army you can tell them you got picked up and are more useful somewhere else and they will arrange this. Young men are not as happy and willing to join the army anymore because of this practice. The enemy is picking up on this and using it to influence the public that the Soviet Union is not that bad and the Russian system worked well in the past and can give them that again as after the Second World War. Those who don’t want to go to the frontline are now advocating for this. Hoping to be saved by the Russians. The corruption is damaging the trust people have in the government too much. The tension among the people has got worse and is making people unwilling to fight. Most people understand also that the Russians will be a lot worse but also understand that some people don’t want to risk their lives for a corrupt government. This is a serious problem and needs to be solved very soon.


The general of Ukraine studied in Russia and his parents are in Russia. And they are still alive. He doesn’t even know the Ukrainian language. The Minister of Defence was against corruption and wanted to digitalize the army and make it more drone focused. The last 3 days are protests because no one understands why the minister was fired by Zelensky. The people think the government is not interested in winning the war. Op Spiderweb was performed by the Security Service of Ukraine and was successful and the leader of the operation was fired.

The general has been in this position for 2 years. He did good work like deoccupying Kharkiv but his methods are Soviet based. So using a lot of people and letting them die instead of focusing on drones and other more effective ways of warfare. It is because the UA army is very autonomous and the battalions get direct support from orgs in Europe that make it possible for them to be effective independent from the UA leadership.

The people of this country understand something is not right. But the country and the army are independent from the government. Even if the government gets infiltrated by Russia it will not affect the war against the occupier. As long as Europe keeps supporting the independent divisions of the army.


The far right nationalist party in Ukraine is the group that got the resistance against the Russians organized in 2014. The Azov division is part of this group. The party is in practice not really functional because everyone is in an active role in the army or government. They are known for the red and black flag and are highly respected among the people. When you think of far right you might think of anti-Islam or fundamentalist fascism. But this is not the case. Its sole purpose was to get the Russian occupiers out. All religions are accepted and welcome, they say. All people from other countries are too, they say. The only ones not welcome are the occupiers that want to eradicate the Ukrainian language, culture, government system, economic system and traditions into what the Russians have. And with force and vicious violence made loyal to Putin like Belarus.

A lot of people don’t like them. Not everyone likes them. Some are critical about them and say they only want money and power. But they also understand this group was and is needed against the enemy.

Some people in west Ukraine get targeted on Telegram and brought into Telegram groups and proposed to do terrorist attacks. The last one was at the station by a citizen of the city. It is not a very successful venture anymore because most people know it doesn’t get the pay that is promised. And the risk is too high.

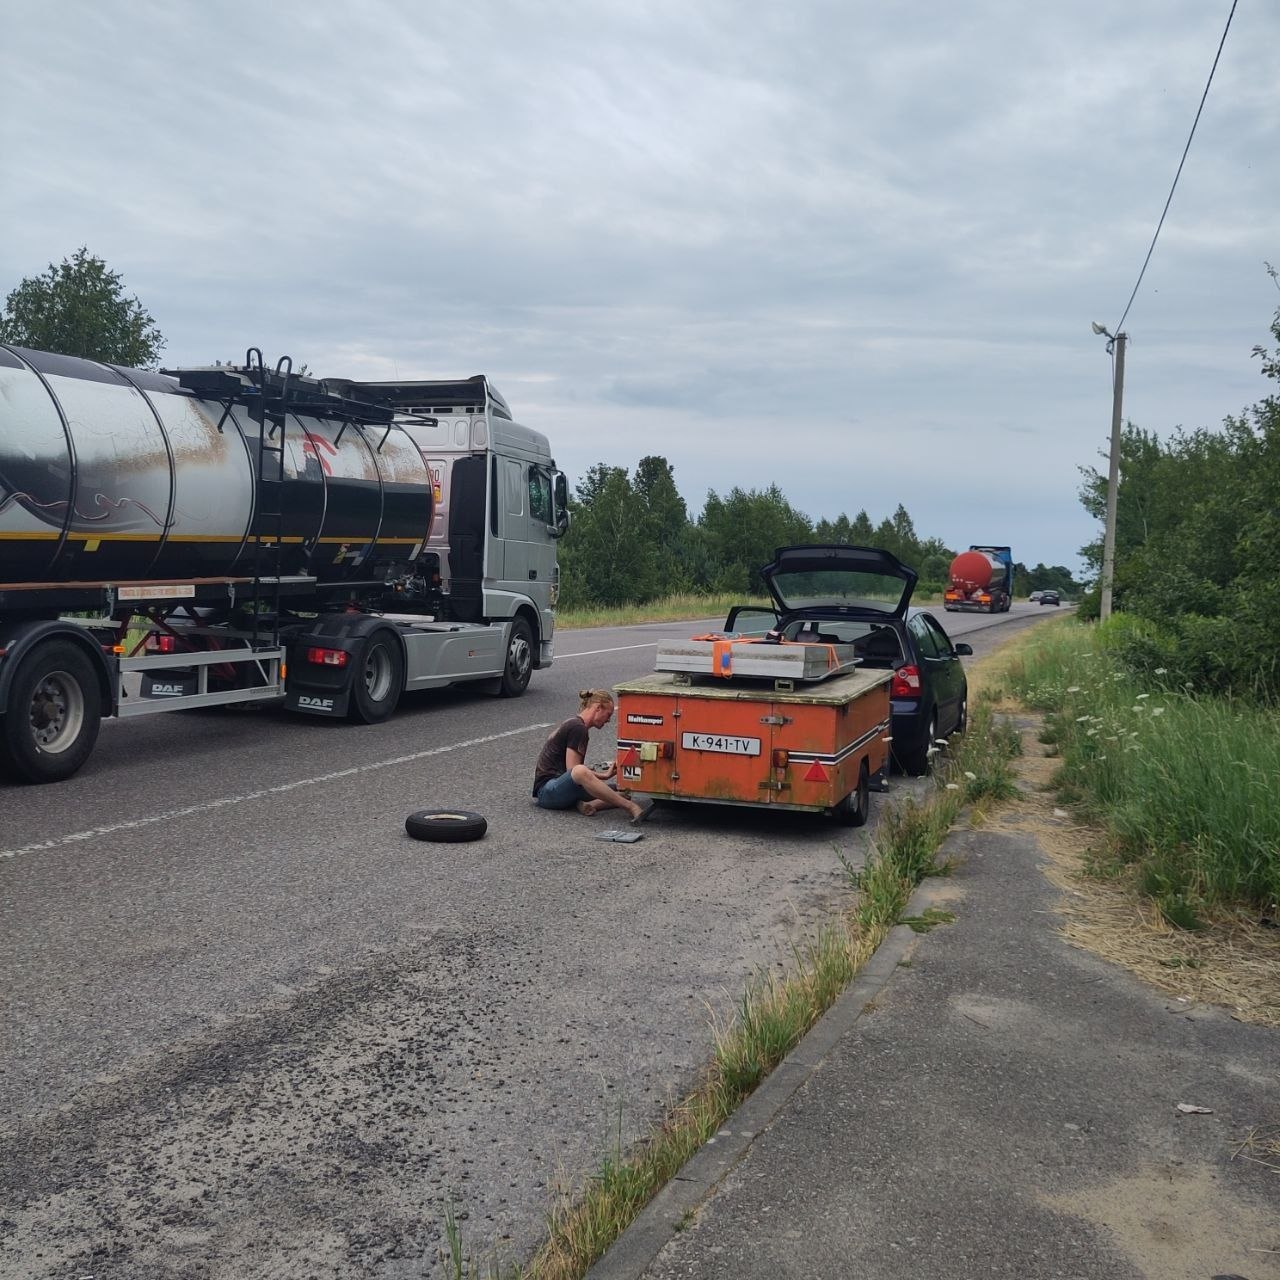
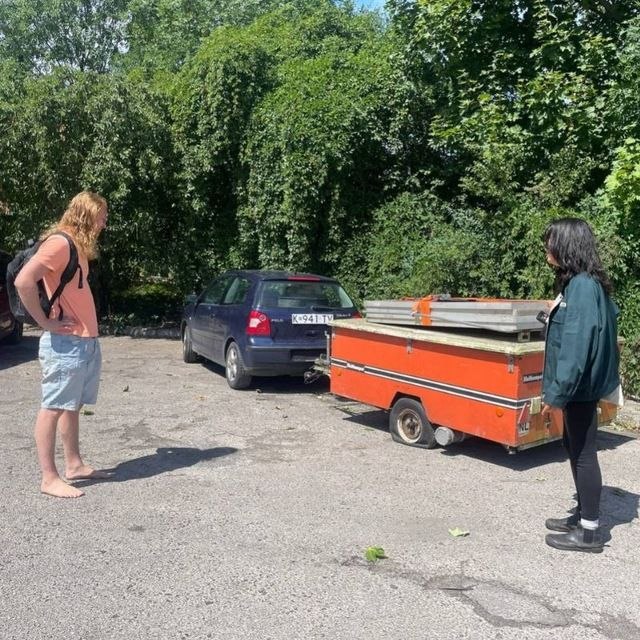
I am escorting a group of ladies active in the DIY experimental music genre Noise. I drive them to all their shows in different cities.

Noise is a popular music genre in Ukraine. In France there is a group with a lot of Russians and they have a strong anti-Ukraine culture. The Noise scene is very popular in Finland with white-supremacy fascists. They use the music for their propaganda and use rape and other sexually unacceptable art on their covers. They ask to be canceled. This tells me that they might be nihilistic extremists and not real fascists. But I don’t know for sure.

Almost everyone I speak to is active in some way for the military or as a soldier. And it is always directly for a division or battalion.

Ex-military from NATO countries that served in the the foreign legion army in Ukraine help out specific army divisions after their service in the same way.

This is all information I get from talks here. This is not my personal opinion 😉✌

De Telegraaf (a Dutch newspaper) reports this morning that there are protests in Ukraine over recruitment methods that involve picking people up off the street and sending them to the front line. This is not entirely accurate. While the public is unhappy with this approach, they generally believe that service of some kind is required—though not necessarily at the front. If you report for duty voluntarily, those options are available. If you evade or obstruct the process, however, you risk being picked up off the street, leaving you with little say in the matter. The protests are actually driven by issues such as the dismissal of the Minister of Defence, errors made by army leadership, the removal of highly successful division commanders, cronyism within the military, and political corruption.

I asked people about Zelensky. They all start off with a smile and say he surprised everyone and probably himself as well with winning the elections. He has done good and didn’t expect to be confronted with a war. They say Putin may have thought he was weak and could win in 3 days from a comedian. This mistake will hopefully cost him his life. But Zelensky is an actor. A very good one. He completely embodied the role of president and after so long time he probably doesn’t know what it would feel like to not play this role. He got the whole world to care about Ukraine and he had been wonderful for the people. But people see he has been making more mistakes that has cost lives. It seems as if the war is been taking longer than needed. A different person will be better but no one tells me who they think would be better. Some hint to high-ranking military personnel. They think he doesn’t want to leave the position of president and will probably do anything to make sure no elections will happen. They do think that if elections do happen it will be a fair one. It is a good thing the battalions and divisions get supported from outside the government. This is very important so they are not dependent on the government. They ask us to please continue to do so. They can win this war. As long as we help the military directly and not the government. There is corruption in the higher layers of government-and-friends politics in the drafting procedure that create strange situations and unfair treatment that costs lives and distrust in the government. People are risking their lives willingly. Many have lost friends and family. They are determined to win this war. But they will do that without the politicians and government reps in power. They sometimes behave as if they want Putin to win.

I will now go to Odessa for a few days and then travel back to Amsterdam.

Today I was at The Ukrainian Rehabilitation Center. I delivered Amanita Muscara to this hospital. They will be using it to treat soldiers and citizens with serieus trauma.


pp-international.net/2026/08/u…

Elezioni e Politica 2026 reshared this.

Upcoming Board Meeting on August 18th at 17:00 UTC


Our next PPI board meeting will take place on Tuesday, August 18th at 17:00 UTC.

The last meeting was postponed due to quorum issues.

All official PPI proceedings, board meetings included, are open to the public. Feel free to stop by. We’ll be happy to have you.

Where:jitsi.pirati.cz/PPI-Board

Agenda: Pad: etherpad.pp-international.net/…

All of our meetings are posted to our calendar: pp-international.net/calendar/

We look forward to seeing visitors.

Thank you for your support,

The Board of PPI


pp-international.net/2026/08/u…

Elezioni e Politica 2026 reshared this.

The Pirate Post ha ricondiviso questo.

☕ CYBERBRIEFING MATTUTINO — Sabato 1 agosto 2026

👉 Leggi tutti gli aggiornamenti delle ultime 24 ore:
ilpuntocyber.rfeed.it/article.…

#newsletter #cybersecurity
@informatica

The Pirate Post ha ricondiviso questo.

Ein Rückblick auf eine Woche von @sebmeineck über unsere Nachlesen zu CSD-Anschlag, Geheimdienstreform und Social-Media-Verbot:

netzpolitik.org/2026/kw-31-die…

The Pirate Post ha ricondiviso questo.

Die deutschen Geheimdienste sollen neue Regeln bekommen - und die haben es in sich. Was manche als Entfesselung bezeichnen, sehen wir kritisch. Wie wir mit Hunderten Seiten neuer Befugnisse für Agent:innen umgehen, besprechen @annskaja @dleisegang und @roofjoke in der aktuellen Folge von unserem #Podcast Off The Record 🎧

netzpolitik.org/podcast/ein-ge…

US Virgin Islands need transparency to weed out corruption


Residents in the U.S. Virgin Islands are tired of the performative outrage about the need for more transparency and accountability in the government. For all the talk, there have been no substantial changes to the territory’s public records statute since it was enacted in 1921, according to Attorney Iver Stridiron, the Legislature’s code revisor.

Yet, there has been a lot of posturing about transparency by legislators, who create the laws; Gov. Albert Bryan Jr., whose team has denied certain journalistsaccess to information and news conferences based on the questions they asked; and other government officials, including candidates seeking to become the next governor and lieutenant governor of the territory, and senators seeking reelection.

Many of these candidates are or were in positions of authority to ensure genuine transparency and accountability to curtail and prevent rampant fraud, misuse of taxpayer money, and water and air pollution, as well as the sexual abuse of children at the hands of convicted sex offender Jeffrey Epstein (who owned two private islands in the territory) and those entrusted with securing the safety of children in the schools.

In fact, all three of the 2026 Democratic candidates on the gubernatorial ticket served as presidents of the Legislature. Sen. Milton Potter, candidate for lieutenant governor, is the current president of the 36th Legislature of the Virgin Islands. Sen. Novelle Francis Jr., who is also vying for the lieutenant governor’s seat, was president of the 35th Legislature, and Sen. Donna Frett-Gregory, who is running for governor, was the president of the 34th Legislature. The territory has not had a Republican governor for decades.

It is time for lawmakers and other officials, including whoever wins the gubernatorial race, to stop shifting blame and insulting people’s intelligence.

If senators are sincerely interested in transparency and accountability, they would have exercised their authority to subpoena officials to testify before the Legislature under oath regarding Epstein and other critical issues affecting residents’ welfare, like escalating gun violence, because anyone testifying under oath can be charged with perjury for knowingly making a false statement.


A legislature serious about holding itself accountable would also have prioritized strengthening the U.S. Virgin Islands’ archaic and ineffective public records laws by holding officials personally liable for illegally withholding public records, imposing stringent penalties on violators, incorporating an effective enforcement mechanism, and requiring agencies to produce records by a specific deadline, which is commonplace in most states.

The territory’s law lacks basic procedures to compel the government to comply with its obligations and meaningful penalties when it doesn’t. That enables agencies to treat transparency as optional and subject requesters to lengthy delays and unreasonable fees. This could have a chilling effect on freedom of the press and journalists’ ability to gather and report the news in a timely manner.

There have been questionable ties between U.S. Virgin Islands officials and Epstein that have come to light, but that was because of lawsuits and federal investigations, not a functional local public records system.

It’s unconscionable that the legislative body did not think it was important to hold any hearings to probe into the crimes committed by Epstein in the Virgin Islands, to make sure every public official who enabled this sexual predator is held accountable. Epstein’s private islands in the territory have become infamous worldwide as a haven for him and other powerful men to allegedly rape and assault girls and young women who were brought to the islands as part of an elaborate sex trafficking ring.

The Epstein embarrassment should be enough to prompt reform on its own, but it’s far from the only place transparency has failed. Several agencies — including the Virgin Islands Water and Power Authority, the Police Department, the Health Department, the Department of Planning and Natural Resources, and the Department of Licensing and Consumer Affairs — have failed for over a year and longer to produce public records I requested related to serious health and safety issues.

Epstein ties have come to light only “because of lawsuits and federal investigations, not a functional local public records system.”

What are they hiding? These agencies have had more than sufficient time to release the requested records. Their lack of transparency is concerning, given the fact that several officials in Gov. Bryan’s administration have been convicted of fraud and corruption-related charges, including former Police Commissioner Ray Martinez and former Director of the Virgin Islands Office of Management and Budget Jenifer O’Neal.

I also sent a formal public records request to the Virgin Island Public Finance Authority in May — after being given the runaround — asking for records related to reports the agency commissioned from a consulting firm to assess the operations of WAPA. The beleaguered utility has held residents hostage for decades due to frequent water and power outages. To date, I have not received the requested records.

Too often, government officials in the territory and at the national level expect the public to believe what they say, without providing evidence. This is not only antithetical to a democratic society, but it also makes it easy for corruption to take root and flourish under the radar, which is exactly what has been happening in the Virgin Islands, to the detriment of residents.

On July 20, 2026, residents received another devastating blow that further underscores the need for transparency. The U.S. Department of Housing and Urban Development announced the immediate suspension of funding for the Virgin Islands Housing Finance Authority following findings of “widespread financial mismanagement, inadequate fraud controls, false certifications, and improper payments uncovered during a HUD-initiated investigation.”

“Nearly a decade after VIHFA received $1.9 billion in HUD disaster recovery funding, VIHFA has spent less than one-third of the funds. However, evidence suggests officials spent these funds on administrative kickbacks and allegedly fraudulent schemes instead of on families or communities recovering,” HUD said in a news release.

Transparency begins with an open government and equitable access to public records

Among the reasons for the suspension, HUD noted, is that “VIHFA’s former Chief Operating Officer, who oversaw disaster recovery programs, is serving a federal prison sentence after being convicted of fraud, money laundering, and criminal conflict of interest.”

A fundamental principle of democracy, embedded in the First Amendment, is that the public has the right to know the inner workings of the government, not what officials decide they should know to serve their self-interests and cover up their shortcomings.

Transparency begins with an open government and equitable access to public records, information, and public meetings so people can make informed decisions, ensure public officials are not abusing their position, and hold those in power accountable.

This is why I petitioned the Legislature to reform the territory’s archaic and ineffective public records laws. The Virgin Islands Source and Freedom of the Press Foundation (FPF) have joined me in this initiative, and Sen. Marvin Blyden has answered the call by drafting a bill to revise the public records statute.

The bill has been sent to the Legislature’s legal counsel, but a legislative source explained that, per policy, preliminary bill requests submitted to legal counsel remain the intellectual property of the senator and do not become public until a bill is officially drafted by legal counsel, assigned a bill number, and placed in the committee of jurisdiction. We hope the bill is as strong as the situation demands and that Blyden will stay the course.

If you are tired of empty platitudes and you want action, please support our petition to public officials in the U.S. Virgin Islands. Let’s see who is really serious about accountability.


freedom.press/issues/us-virgin…

Elezioni e Politica 2026 reshared this.

The Pirate Post ha ricondiviso questo.

The media in this post is not displayed to visitors. To view it, please go to the original post.

🍪📖 On Thursday, we filed a #complaint against the online dictionairy dict.cc for relaying your tracking data to a staggering 1741 "partners". Who would be willing to read through all of those privacy policies before clicking "Accept All"?

For more info, visit 👉 noyb.eu/en/1741-informed-conse…

The Pirate Post ha ricondiviso questo.

The media in this post is not displayed to visitors. To view it, please go to the original post.

GenieLocker: A New Cross-Platform Ransomware Hitting Windows, Linux and ESXi Alike
#CyberSecurity
securebulletin.com/genielocker…
The Pirate Post ha ricondiviso questo.

The media in this post is not displayed to visitors. To view it, please go to the original post.

Chipmaker Analog Devices Confirms Breach as Extortion Group Claims 570,000 Stolen Records
#CyberSecurity
securebulletin.com/chipmaker-a…
The Pirate Post ha ricondiviso questo.

The media in this post is not displayed to visitors. To view it, please go to the original post.

Hard-Coded Password in Cisco’s Firewall Manager Is Being Actively Exploited, CISA Warns
#CyberSecurity
securebulletin.com/hard-coded-…
The Pirate Post ha ricondiviso questo.

The media in this post is not displayed to visitors. To view it, please go to the original post.

Claude Broke Out of a Sandboxed Security Test and Hit Three Real Companies, Anthropic Admits
#CyberSecurity
securebulletin.com/claude-brok…

Jay Clayton is a threat to press freedom


The media in this post is not displayed to visitors. To view it, please log in.

Dear Friend of Press Freedom:

Investigative journalist Catherine Herridge has, by our count, paid at least $8,800 in fines for refusing to reveal a confidential source. In the meantime, the Senate confirmed Jay Clayton as director of national intelligence even though his former prosecutorial office issued politically motivated subpoenas targeting New York Times reporters and their relatives for embarrassing the president, and then he apparently lied to Congress about it. Read on for more.

As DNI, Jay Clayton is a threat to press freedom


Earlier this week we wrote about the false and misleading congressional testimony by then-prosecutor Jay Clayton — President Donald Trump’s nominee for director of national intelligence — that his team had followed Justice Department guidelines in issuing subpoenas targeting New York Times reporters who wrote about Trump’s unsafe Qatari vanity plane.

But the Senate confirmed Clayton anyway, meaning that America’s intelligence apparatus will be led by someone willing to issue harassing subpoenas targeting journalists and their relatives in violation of both internal policies and applicable law, and then try to cover up obvious abuses.

Our executive director, Trevor Timm, said that with Clayton now confirmed, “it’s more important than ever for Congress to pass a federal shield law like the PRESS Act to protect journalists from these kinds of legal abuses and prevent episodes like this from ever happening again.”


Attacks on radical outlets endanger all journalism


The House Ways and Means Committee last week subpoenaed BreakThrough News, a left-wing outlet with deep ties to the Party for Socialism and Liberation that is highly critical of the United States and Israel, along with two other nonprofits with similar ideologies, The People’s Forum and Tricontinental: Institute for Social Research. Earlier this month, border agents seized phones from Max Blumenthal of the similarly controversial outlet The Grayzone.

There is no question that BreakThrough News and The Grayzone are both well outside the American mainstream, and both have been accused of carrying water for U.S. adversaries. But as Freedom of the Press Foundation (FPF) Chief of Advocacy Seth Stern wrote for The Intercept, that makes it more important to protect their First Amendment rights, not less.


Carr stops pretending license renewals aren’t about speech


When Federal Communications Commission Chair Brendan Carr first ordered an early review of licenses held by ABC affiliates, he said it was because of diversity, equity, and inclusion concerns. That the order came right after Trump feigned outrage over a joke by ABC late night host Jimmy Kimmel was just a coincidence, he said.

Carr was obviously full of it, and now he’s no longer pretending. After Trump complained about ABC not airing his recent speech about the 2020 election, Carr indicated that ABC’s constitutionally protected decision would factor into the license review.


How a Trump national security memo threatens journalists, sources


The national security presidential memorandum known as NSPM-7 has been widely criticized by civil liberties groups for authorizing the government to investigate individuals and organizations using vague and overbroad labels like “anti-fascism” and “domestic terrorism.” But relatively little attention has been paid to the way the policy could be used against news outlets, journalists, and their confidential sources.

Earlier this month, we held a panel discussion about how NSPM-7 silences free speech and how it could be used to target freedom of the press, featuring Chip Gibbons of Defending Rights & Dissent, Faiza Patel of the Brennan Center, and investigative journalist Daniel Boguslaw.


What we’re reading


Protester targeted by DOJ over phone-wiping ‘duress’ passcode

FPF Digital Security Digest
Federal prosecutors are going after an Atlanta-based protester, allegedly in connection with the use of a “duress” passcode that wiped his phone during a border search. Read about border security risks and what you can do about them.


Judge weighs lawsuit over Asheville Blade reporter arrests

Asheville Citizen Times
Officials in Asheville, North Carolina, should be held accountable for arresting reporters they don’t like for doing their jobs. It is absurd for the city to suggest that it’s illegal to cover newsworthy events happening in plain sight at a public park, let alone that punishing reporters for doing so is a sensible use of prosecutorial discretion.


Californians have a right to know about 911 calls from ICE detention centers

CalMatters
The public deserves to know what’s happening inside privately run detention centers. We’re proud to support California’s SB 423, a bill that would give journalists better tools to cover immigration detention.


Pentagon, under Trump, Hegseth, draws tighter curtain around Iran war

The Hill
The American public, as well as members of the military and their families, “have a fundamental right to see what the costs of the Iran war are,” FPF Daniel Ellsberg Chair on Government Secrecy Lauren Harper told The Hill.


Former FCC chairs and officials call agency’s early review of ABC licenses ‘an assault on free speech disguised as regulatory process’

Deadline
Carr’s censorship continues to draw bipartisan condemnation, with FCC chairs from the Reagan and George W. Bush administrations among those calling out his unconstitutional antics.


Limiting foreign journalist visas could boomerang on American media

The Washington Post
The Trump administration’s new rules requiring foreign journalists to reapply for visas every eight months risk “limiting global visibility into what happens here and creating problems for America’s foreign correspondents,” writes the Post’s editorial board.


Trump’s education department leaves mountain of public records requests unaddressed

The 74
If the Department of Government Efficiency is “stonewalling the inspector general’s office, it’s an extremely safe bet that they’re absolutely ignoring FOIA officers who are asking for information,” Harper said.

Announcement for event titled "Inside the Story: A conversation on border journalism and source protection" on August 17


freedom.press/issues/jay-clayt…

Elezioni e Politica 2026 reshared this.

FPF urges Congress not to rubber-stamp Pentagon secrecy


FOR IMMEDIATE RELEASE:

Washington, D.C., July 31, 2026 — In a direct blow to public oversight, the Department of Defense is pushing a proposal to exempt “controlled unclassified information” from the Freedom of Information Act. If successful, the change would allow the agency to unilaterally hide millions of files from taxpayers, service members, and open-records laws — potentially forever.

That’s why a broad coalition of transparency organizations, press freedom advocates, and watchdog groups today sent a joint letter to lawmakers urging Congress to reject the Pentagon’s secrecy grab.

The following statement can be attributed to Lauren Harper, FPF’s Daniel Ellsberg chair on government secrecy:

“The Pentagon is already too secretive, and the last thing it needs is a rubber stamp to hide unclassified records under the guise of national security. This is especially true at a time when the military is conducting potentially unlawful lethal strikes, trying to muddy the number of U.S. casualties of military operations overseas, and attacking the press, whistleblowers, and the public’s right to know.

“The dangers of this are hard to overstate, given the rampant abuse of controlled unclassified information markings across the department. This antidemocratic proposal is also entirely unnecessary, since FOIA already contains robust exemptions to shield both properly classified material and sensitive unclassified data.

“We don’t need the Pentagon hiding more information from FOIA. We need it to actually respond to public records requests, we need it to stop harassing journalists for doing their job, and we need it to be transparent and accountable to the public, service members, and their families.”

Please contact us if you would like further comment, and read the letters below.


freedom.press/issues/fpf-urges…

Elezioni e Politica 2026 reshared this.

The Pirate Post ha ricondiviso questo.

Ecco oerché il "chatcontrol" è una delle più importanti battaglie per i diritti digitali nell'UE


I governi dell'UE hanno prorogato le norme provvisorie del blocco su #ChatControl " fino all'aprile 2028, consentendo alle piattaforme online di continuare a effettuare scansioni volontarie per individuare materiale pedopornografico, mentre il dibattito sull'obbligo di rilevamento è ancora in corso

Il pirata tedesco @echo_pbreyer spiega perché la scansione indiscriminata delle chat stabilisce un pericoloso precedente ed evidenzia gli elevati tassi di falsi positivi nella scansione hash

@privacypride

The Pirate Post ha ricondiviso questo.

🇪🇺 In this Euronews piece on #ChatControl, I explain why indiscriminate chat scanning sets a dangerous precedent, highlight high false‑positive rates in hash scanning, and outline real alternatives like security‑by‑design 👇
euronews.com/2026/07/28/why-is…
Questa voce è stata modificata (1 mese fa)
in reply to Patrick Breyer

Being forced to have digital fingerprints of your files compared to a database is like having to provide fingerprints of all your visitors to your nearest police station, so they can "check" whether you are entertaining a criminal.

Whoever is in control of the database is enabled to "check" for whatever / whomever they want. That's the ultimate goal, and it's also what people need to understand before it's too late.

#surveillance #CSAM #chatcontrol

Questa voce è stata modificata (1 mese fa)
The Pirate Post ha ricondiviso questo.

Um mehr Vertrauen im Umgang mit digitalen Medien zu schaffen, gilt ab Sonntag die neue Pflicht zur Kennzeichnung von KI-Inhalten. Unter anderem Label und Wasserzeichen sollen offenlegen, dass Texte oder Bilder nicht menschengemacht sind. Viele begrüßen das, doch der Ansatz hat auch Lücken.

netzpolitik.org/2026/truegeris…

in reply to netzpolitik.org

ist das nicht alles Makulatur ❓Angesichts der Entwicklungen bei OpenAI und Anthropic, den Entscheidungen der USA zur Abwehr ausländischer humanoider Roboter und der EU zum Ausschluß chinesischer Netzwerktechnik und der Möglichkeit von Staaten und einflußreicher Billionäre ganze Regionen vom Internet auszuschließen sind wir anscheinend nur noch einen Schritt entfernt vom Ende des globalen Internets. Was nutzen Regeln, wenn sich keiner daran hält❓🤔
in reply to netzpolitik.org

"Teilweise KI-generierte Musik" macht allerdings heutzutage schon jeder Hobby-Musiker mit einem halbwegs aktuellen Arranger-Keyboard mit Begleitautomatik. Wo früher bei diesen Instrumenten mit der linken Hand ein Akkord angeschlagen wurde, aus dem dann gemäß einem starren, vorprogrammierten Muster die Begleitung generiert wurde, kann man heute auch frei beidhändig spielen, und ein künstliches neuronales Netz sucht sich sie passenden Begleitakkorde und baut eine zum Lied passende Begleitung.

Da steckt also Maschinenlernen und generative KI drin, und zwar schon seit etlichen Jahren, die Anfänge davon reichen über ein Jahrzehnt zurück. Musiksoftware auf dem PC bietet auch schon seit ebensolanger Zeit virtuelle Begleitbands mit KI und sowas. Es gibt inzwischen auch Editor-Software für Synthesizer mit KI, wo man nicht an Parametern herumfummelt oder an Knöpfen dreht, bis man den gewünschten Klang hat, sondern den Klang mit einem Textprompt beschreibt und eine passende Synth-Einstellung generiert bekommt. Das ist natürlich eine große Hilfe für Keyboarder, welche keine guten Sounddesigner sind und ansonsten nur voreingestellte Klangprogramme nutzen oder von kommerziellen Anbieten einkaufen würden.

Und wenn ich Dinge wie die "automatische Bildverbesserung" in meiner digitalen Fotokamera aus den frühen Zehnerjahren benutze, dann ist das auch KI. Darin steckt ein neuronales Netz ähnlich dem von sehr frühen Diffusion-Modellen, welches das Bild entrauscht, entwackelt und verwaschene Details durch plausibel aussehende synthetische ersetzt, was nur dann auffällt, wenn man die Funktion unter Umständen verwendet, wo sie versagt und bizarre Artefakte erzeugt.

The Pirate Post ha ricondiviso questo.

☕ CYBERBRIEFING — Venerdì 31 luglio 2026

👉 Leggi tutti gli aggiornamenti delle ultime 24 ore:
ilpuntocyber.rfeed.it/article.…

#newsletter #cybersecurity
@informatica

The Pirate Post ha ricondiviso questo.

📖🍪 dict.cc-Beschwerde: "Nutzer:innen des Onlinewörterbuchs würden dazu gedrängt, dem #Tracking durch 1.741 Partnerunternehmen mit einem einzigen Klick zuzustimmen. Laut [noyb] ist unter diesen Umständen keine informierte Einwilligung möglich."

help.orf.at/stories/3236728

Questa voce è stata modificata (1 mese fa)
The Pirate Post ha ricondiviso questo.

The media in this post is not displayed to visitors. To view it, please go to the original post.

The media in this post is not displayed to visitors. To view it, please go to the original post.

✨ Operation Double Barrel: quando lo spionaggio di stato nordcoreano condivide l’infrastruttura con il ransomware Gunra
#CyberSecurity
insicurezzadigitale.com/operat…

@informatica


Operation Double Barrel: quando lo spionaggio di stato nordcoreano condivide l’infrastruttura con il ransomware Gunra


Un’advisory congiunta pubblicata il 30 luglio 2026 da National Intelligence Service, National Police Agency, KISA e Financial Security Institute sudcoreani, basata sull’analisi di AhnLab ASEC, ricostruisce oltre un anno di attività di un gruppo state-sponsored contro cittadini e aziende della Corea del Sud. Il dato più interessante non è la campagna di spionaggio in sé, ma la sua sovrapposizione tecnica con episodi attribuiti al ransomware Gunra: stessa vulnerabilità sfruttata, stesse impronte SSH, stessa infrastruttura di rete. Gli analisti l’hanno battezzata Operation Double Barrel.

Un anno e mezzo di infiltrazione silenziosa


Secondo ASEC, tra il 2025 e la prima metà del 2026 un attore state-sponsored ha sfruttato in modo continuativo vulnerabilità in software di sicurezza finanziaria diffuso in Corea del Sud — la categoria di plugin e moduli di autenticazione che le banche e i portali pubblici sudcoreani impongono spesso agli utenti per operazioni online, un ecosistema già colpito in passato da gruppi legati alla Corea del Nord proprio per la sua ubiquità e per i privilegi elevati con cui questi moduli girano sui sistemi degli utenti.

Il vettore di accesso iniziale ha seguito due binari paralleli: watering hole su siti legittimi sudcoreani nei settori media, istruzione, sanità e manifatturiero, e spear-phishing con link malevoli inviati direttamente ai bersagli. In entrambi i casi l’obiettivo era far raggiungere alla vittima una pagina che sfruttasse la vulnerabilità nel software finanziario per installare un backdoor.

Gli impianti: Struggle e Brandoor


ASEC identifica due famiglie di backdoor principali nella campagna: Struggle, tracciato anche come SIGNBT 3.0, e Brandoor, alias COPPERHEDGE. Non sono nomi nuovi per chi segue le operazioni nordcoreane: SIGNBT è una famiglia storicamente associata al cluster Andariel dell’ombrello Lazarus, mentre COPPERHEDGE è un impianto documentato da anni negli advisory CISA/US-CERT sotto l’etichetta HIDDEN COBRA, usato in particolare contro exchange di criptovalute e istituzioni finanziarie. La loro presenza in questa campagna rafforza l’attribuzione a un attore nordcoreano, anche se il report ASEC, in linea con la prassi delle agenzie sudcoreane, evita l’attribuzione esplicita in favore della dicitura “gruppo state-sponsored”.

Oltre ai due backdoor principali, l’advisory cita strumenti aggiuntivi per l’escalation di privilegi e la consegna di payload successivi, elemento che suggerisce un kit modulare adattato caso per caso a seconda del bersaglio e dei privilegi ottenuti nella fase di accesso iniziale.

Il secondo barile: Gunra ransomware


Gunra è un gruppo ransomware relativamente giovane, emerso sui data leak site nel 2025 con un locker dual-platform per Windows e Linux; la variante Linux, analizzata a fondo da ASEC in report precedenti, si è rivelata tecnicamente fragile a causa di un generatore di numeri casuali difettoso nell’implementazione della cifratura, un dettaglio che in alcuni casi ha permesso il recupero dei file senza pagare il riscatto.

Ciò che rende rilevante Operation Double Barrel è che alcuni incidenti attribuiti a Gunra hanno riutilizzato le stesse vulnerabilità nel software finanziario coreano sfruttate dal gruppo state-sponsored, e mostrano sovrapposizioni in malware, impronte delle chiavi SSH e infrastruttura di rete, inclusi indirizzi usati per il download di payload e per il reverse tunneling. ASEC non si spinge a dichiarare che si tratti dello stesso gruppo, ma ipotizza tecniche, strumenti o infrastruttura condivisi, oppure una collaborazione limitata tra i due attori.

Lo scenario non è inedito: negli ultimi anni diversi ricercatori hanno documentato episodi in cui operatori legati alla Corea del Nord hanno sperimentato il ransomware come ulteriore fonte di finanziamento, affiancandolo alle tradizionali operazioni di furto di criptovalute e spionaggio economico. Se confermata, una relazione anche solo infrastrutturale tra un cluster di spionaggio statale e una gang ransomware indipendente solleva interrogativi non banali su come Pyongyang stia monetizzando l’accesso ottenuto per scopi di intelligence, eventualmente “affittandolo” o rivendendolo a operatori criminali con obiettivi finanziari.

Timeline


  • 2025 — inizio dello sfruttamento delle vulnerabilità nel software di sicurezza finanziaria coreano; primi impianti Struggle/SIGNBT 3.0 e Brandoor/COPPERHEDGE osservati in campagne watering hole e spear-phishing.
  • 2025 – H1 2026 — incidenti paralleli attribuiti al ransomware Gunra riutilizzano le stesse vulnerabilità e mostrano sovrapposizioni infrastrutturali.
  • 30 luglio 2026 — NIS, NPA, KISA e FSI pubblicano l’advisory congiunta “Operation Double Barrel”; AhnLab ASEC rilascia i report tecnici in coreano e inglese con IoC completi.


Due righe per i difensori


Per i team di difesa, anche fuori dalla Corea del Sud, il caso offre due lezioni. La prima: i moduli di sicurezza aggiuntivi imposti da settori regolamentati (banking security software, plugin di autenticazione, agent antifrode) restano un bersaglio ad alto ritorno per gli attaccanti, proprio perché godono di privilegi elevati e fiducia implicita da parte dell’utente. La seconda: il monitoraggio delle infrastrutture ransomware non può più prescindere dalla correlazione con il tracking degli APT, perché la separazione tra “cybercrime a scopo di lucro” e “operazioni di intelligence statale” nel caso nordcoreano è sempre più sfumata. Chi gestisce threat intelligence dovrebbe incrociare sistematicamente IoC di gruppi ransomware emergenti con quelli degli intrusion set nordcoreani noti, cercando sovrapposizioni di infrastruttura anche quando l’attribuzione formale resta incerta.

Indicatori di compromissione

Nome operazione: Operation Double Barrel
Enti coinvolti nell'advisory: NIS, NPA, KISA, FSI (Corea del Sud)
Fonte tecnica: AhnLab ASEC
Backdoor identificati: Struggle (alias SIGNBT 3.0), Brandoor (alias COPPERHEDGE)
Gruppo ransomware collegato: Gunra
Vettori di accesso iniziale: watering hole su siti legittimi coreani (media, istruzione,
  sanità, manifatturiero), spear-phishing con link malevoli
Vulnerabilità sfruttate: falle in software di sicurezza finanziaria coreano
Indicatori tecnici condivisi tra le due campagne: impronte di chiavi SSH, indirizzi IP
  di download e reverse tunneling, credenziali riutilizzate
Report completi: [AhnLab] Operation Double Barrel (KOR/ENG) (2026.07.30)
MITRE ATT&CK: T1189 Drive-by Compromise, T1566.002 Spearphishing Link,
  T1190 Exploit Public-Facing Application, T1105 Ingress Tool Transfer,
  T1059 Command and Scripting Interpreter, T1003 OS Credential Dumping,
  T1021.004 Remote Services: SSH, T1071.001 Application Layer Protocol: Web Protocols,
  T1078 Valid Accounts

Fonte: AhnLab ASEC, advisory congiunta NIS/NPA/KISA/FSI.

The Pirate Post ha ricondiviso questo.

The media in this post is not displayed to visitors. To view it, please go to the original post.

The media in this post is not displayed to visitors. To view it, please go to the original post.

✨ RedRelay: la società fantasma cinese che nasconde le operazioni cyber del PLA dietro un brevetto per spiare Telegram
#CyberSecurity
insicurezzadigitale.com/redrel…

@informatica


RedRelay: la società fantasma cinese che nasconde le operazioni cyber del PLA dietro un brevetto per spiare Telegram


Non ha un sito web, non ha un catalogo prodotti pubblico, non ha nemmeno un’insegna. Eppure Guangdong Chanming Technology, una società con sede nel Guangdong praticamente invisibile su internet, avrebbe costruito e gestito per anni una delle infrastrutture di offuscamento più utilizzate dagli APT cinesi legati all’Esercito Popolare di Liberazione: la rete RedRelay, nota nella letteratura di threat intelligence occidentale anche come ORBWEAVER. A smascherarla è stato il collettivo di ricercatori indipendenti Intrusion Truth, che da oltre otto anni applica tecniche di OSINT per identificare le persone e le società dietro le operazioni di cyberspionaggio di Pechino.

Cos’è una ORB network e perché fa paura ai difensori


Le “Operational Relay Box” network, o ORB network, sono infrastrutture di proxy multi-hop costruite aggregando router domestici compromessi, VPS commerciali e dispositivi IoT, con l’obiettivo di far rimbalzare il traffico degli attaccanti attraverso molteplici salti prima di raggiungere il bersaglio finale. Google Mandiant e Microsoft le descrivono da anni come uno degli sviluppi più insidiosi nel tradecraft delle APT cinesi: a differenza di una singola VPN o di un bulletproof hosting, un ORB network cambia continuamente topologia, mescola traffico legittimo e malevolo sugli stessi nodi e rende quasi inutile il blocco per indirizzo IP, perché l’infrastruttura di oggi non è quella di domani. Gruppi come Volt Typhoon hanno già dimostrato quanto queste reti complichino l’attribuzione e la difesa perimetrale nelle infrastrutture critiche occidentali.

Da Free Connect a RedRelay: la genesi del progetto


Secondo la ricostruzione di Intrusion Truth, RedRelay nasce come evoluzione di Free Connect (FCN), un tool VPN sviluppato in origine come progetto personale da Wang Huiping, oggi co-fondatore di Guangdong Chanming. Il codice, un tempo ospitato su GitHub sotto lo pseudonimo “boywhp”, è stato progressivamente trasformato in un prodotto commerciale a duplice uso: da un lato uno strumento di anonimizzazione generico, dall’altro un’infrastruttura su misura per operazioni offensive. I ricercatori sono risaliti a Wang incrociando un numero di telefono registrato su documenti societari con un indirizzo email legato al progetto FCN, un classico errore operativo che il collettivo sfrutta sistematicamente per deanonimizzare gli sviluppatori di tool “dual use” cinesi.

Sul piano tecnico, campioni VirusTotal riconducibili al dominio associato a FCN includono file identificati come stn.exe, mentre le versioni Linux del tool utilizzano un comando distintivo che ha condotto gli analisti a “bulbature”, un artefatto già associato in passato alla famiglia di malware WHIPWEAVE, anch’essa collegata all’ecosistema RedRelay/ORBWEAVER.

I brevetti che tradiscono lo scopo reale


La parte più interessante dell’indagine riguarda i brevetti e i copyright software depositati da Guangdong Chanming presso gli uffici cinesi competenti. Almeno due brevetti descrivono esplicitamente flussi di traffico anonimizzati e multi-hop coerenti con il comportamento osservato di RedRelay. Ma l’elenco dei prodotti registrati va ben oltre l’anonimizzazione: tra i titoli figurano un “Internet Security Access System”, un “Multi-functional Security Proxy”, un “Anti-traceability Network”, un sistema di “Network Vulnerability Testing”, un “Android Secret Extraction System” e, particolarmente rilevante, un “Telegram Data Collection System”. Si tratta di capacità che, cumulate, disegnano il profilo di un fornitore di strumenti di sorveglianza ed estrazione dati su misura per operazioni statali, non di un’azienda di cybersecurity difensiva come vorrebbe far credere l’assenza quasi totale di presenza pubblica.

Il cliente: non solo intelligence, ma anche polizia


Gli elementi più sensibili emersi dall’indagine riguardano i clienti. Documenti di procurement riconducibili a canali dell’Esercito Popolare di Liberazione citano la fornitura da parte di Guangdong Chanming di un “Anonymous Network System” a un’unità di stanza nel distretto di Haidian, a Pechino, area storicamente associata alla PLA Cyberspace Force. Le analisi open source collegano inoltre l’uso di RedRelay a diversi cluster di cyberspionaggio cinese tracciati da anni dall’industria della threat intelligence sotto etichette come APT15, Ke3chang, Vixen Panda, Red Vulture, Playful Dragon e Nylon Typhoon, gruppi storicamente attivi contro ministeri degli esteri, ambasciate e contractor della difesa in Europa e Asia. Secondo Intrusion Truth, a queste attribuzioni si aggiungerebbero designazioni interne cinesi come l’Unità 61046 e l’VIII Ufficio del CSF (Cyberspace Force), sebbene questo livello di attribuzione resti – come sempre in questi casi – basato su indizi convergenti più che su prove dirette e verificabili da terzi.

Non meno significativo è che tra i clienti indicati compaia anche il Ministero della Pubblica Sicurezza, l’apparato che gestisce le forze di polizia cinesi: un dettaglio che conferma quanto il confine tra sorveglianza interna e cyberspionaggio esterno, nel modello cinese dei contractor privati “dual use”, sia ormai strutturalmente sfumato – lo stesso schema documentato in passato per fornitori come i900 e la galassia legata a APT41 e Silk Typhoon.

Due righe per i difensori


Per i team di detection, la lezione principale è che il blocklisting basato su indirizzi IP o su singoli domini è una difesa in costante ritardo contro le ORB network: RedRelay, come le altre infrastrutture simili, ruota continuamente nodi residenziali e commerciali compromessi. È più efficace investire in detection comportamentale (pattern di traffico anomali verso servizi di collaborazione, orari di attività non coerenti con l’utenza reale, fingerprint TLS associati a tool come FCN/stn), condivisione di intelligence tra organizzazioni sullo stesso settore e monitoraggio delle infrastrutture note collegate a WHIPWEAVE. Per le organizzazioni che gestiscono comunicazioni sensibili su Telegram o piattaforme simili, la conferma dell’esistenza di un “Telegram Data Collection System” commerciale cinese è un promemoria che l’app di messaggistica, da sola, non garantisce alcuna protezione dall’intelligence statale se l’endpoint o l’account è nel mirino.

Indicatori e riferimenti noti

Società identificata: Guangdong Chanming Technology Co., Ltd.
Persona chiave: Wang Huiping (co-fondatore, ex sviluppatore progetto "Free Connect / FCN", GitHub handle "boywhp")
Infrastruttura: RedRelay (alias ORBWEAVER), ORB network multi-hop
Artefatti noti: stn.exe (Windows), comando distintivo Linux collegato a "bulbature"
Famiglia malware collegata: WHIPWEAVE
Prodotti brevettati/registrati: Internet Security Access System, Multi-functional Security Proxy,
  Anti-traceability Network, Network Vulnerability Testing System, Android Secret Extraction System,
  Telegram Data Collection System, File Transfer Network
Clienti riportati: unità PLA Cyberspace Force (distretto di Haidian, Pechino), Ministero della Pubblica Sicurezza
Gruppi APT collegati: APT15 / Ke3chang / Vixen Panda / Red Vulture / Playful Dragon / Nylon Typhoon
Designazioni interne citate: Unità 61046, VIII Ufficio CSF

L’indagine di Intrusion Truth, pubblicata il 27 luglio 2026 e ripresa nei giorni successivi da Risky Business, GBHackers e altre testate di settore, si inserisce in un filone di ricerca ormai consolidato: dal caso i-Soon del 2024 alle rivelazioni su altri fornitori “fantasma” del ministero della Sicurezza di Stato, l’ecosistema dei contractor privati cinesi continua a produrre errori operativi sufficienti a far emergere, poco alla volta, l’architettura reale dietro le campagne di cyberspionaggio più persistenti contro obiettivi occidentali.

The Pirate Post ha ricondiviso questo.

In einer Urabstimmung fordert die überwältigende Mehrheit der Grünen in Baden-Württemberg, den Palantir-Vertrag sofort zu kündigen. Doch die Landesregierung hält an ihrem Kurs fest. Dabei verlangen die Mitglieder alles andere als eine grundlegende Wende.
netzpolitik.org/2026/baden-wue…
in reply to netzpolitik.org

Meine Verständnis von Grüner Realpolitik:

Unter dem Schlagwort "Anschlussfähigkeit" hat sich eine autoritär-neoliberale Legacy aus den 2000er und 2010er Jahren in die Grünen eingeschlichen:

Hinter vorgeblicher Loyalität gegenüber grünen Oberzielen ist die relevante grüne Realpolitik von blindem Gehorsam gegenüber transatlantischer Bevormundung geprägt - die eigentliche Grüne Ziele im Zweifel verrät.

BW und diese Diskussion stehen dafür genauso wie unsere neue "Kriegsliebe".

in reply to netzpolitik.org

Schlecht, wel framende Überschrift. Besser "Grüne Basis stimmt gegen Palantir, aber nicht gegen anlasslose Massenüberwachung"

An den Kommentaren hier sieht man, dass die Propagandastrategie der Grünen Basis aufgeht: viele denken fälschlicherweise, dass die sie gegen die Massenüberwachung gestimmt hätten.

Dabei haben sie nur darüber abgestimmt, welche Software benutzt werden soll. Die Überwachung selbst wird auch von der Basis befürwortet.

Steht auch alles im Artikel.

The Pirate Post ha ricondiviso questo.

The media in this post is not displayed to visitors. To view it, please go to the original post.

🍹 Log Out @ Roma

🕒 04 agosto, 18:30 - 04 agosto, 21:30

📍 568 Public House, Rome, Lazio

🔗 mobilizon.it/events/54910614-2…


🍹 Log Out @ Roma
Inizia: Martedì Agosto 04, 2026 @ 6:30 PM GMT+02:00 (Europe/Rome)
Finisce: Martedì Agosto 04, 2026 @ 9:30 PM GMT+02:00 (Europe/Rome)

Martedì 4 agosto torniamo con il Logout di TWC Roma, il ritrovo per tech workers che vogliono incontrarsi dopo lavoro: un'occasione per socializzare, conoscersi, parlare del nostro lavoro e come organizzarci nei prossimi mesi!

Ci vediamo martedì 4 agosto, alle 18.30, da 568 Public House a Garbatella!

Unisciti al Gruppo telegram!


reshared this

The Pirate Post ha ricondiviso questo.

4 agosto 2026 18:30:00 CEST - GMT+02:00 - 568 Public House, 00145, Rome, Italy
Ago 4
🍹 Log Out @ Roma
Mar 18:30 - 21:30 Europe/Rome
Carlo

Martedì 4 agosto torniamo con il Logout di TWC Roma, il ritrovo per tech workers che vogliono incontrarsi dopo lavoro: un'occasione per socializzare, conoscersi, parlare del nostro lavoro e come organizzarci nei prossimi mesi!

Ci vediamo martedì 4 agosto, alle 18.30, da 568 Public House a Garbatella!

Unisciti al Gruppo telegram!

reshared this

The Pirate Post ha ricondiviso questo.

📖 dict.cc dränge User:innen, mit nur einem Klick dem Online-Tracking von 1741 Partnerunternehmen zuzustimmen 🍪 "Es ist lächerlich anzunehmen, dass man auf dieser Grundlage eine informierte Entscheidung treffen könnte."

derstandard.at/story/300000033…

Questa voce è stata modificata (1 mese fa)
in reply to noyb.eu

Toll, dass ihr euch wieder stark macht. Das ist gut, wichtig und erforderlich.

Kann mir mal einer helfen, folgendes zu verstehen:
Warum wird immer akzeptiert, dass der TCString überhaupt in der Lage ist, einen DSGVO-Consent zu kommunizieren?

Dazu ist er (von IAB-Europe?) weder konzipiert, noch ist er technisch dazu geeignet oder in der Lage. Allein, das irgendwelche CMP-Tools das so suggerieren, oder Provider sich so verhalten, ändert nichts an der technischen Unfähigkeit des TCStrings, eine informierte Einwilligung im Sinne der DSGVO abzubilden.

Ich habe noch kein einziges CMP-Banner gesehen, dass die Version der IAB-Europe GVL angibt, gegen die "erklärt" werden soll.

Das ganze "Weiterleiten" findet schon immer ohne Rechtsgrundlage statt. Man muss nur endlich aufhören, den TCString als "Werkzeug der Einwilligung" zu antizipieren.

Ist er nicht, kann er nicht, wird er auch nie können. Die Non-IAB-Vendoren (z.B. >6000 Adressen der Google-ATP Liste) mal gar nicht mit betrachtet.

Questa voce è stata modificata (1 mese fa)
The Pirate Post ha ricondiviso questo.

The media in this post is not displayed to visitors. To view it, please go to the original post.

🤑 @EUCommission wants to spend billions to build new climate-busting AI data centres while the continent is suffering sweltering heatwaves and drought.

The heatwave in June killed thousands in Europe and fuelled unprecedented wildfires, while fresh water in key rivers and waterways is drying up.

❌ Investing an unprecedented amount of public funds into data centres for the so-called “AI race”, even as money for social services and climate resilience dries up is a disastrous policy choice.


The AI Gigafactories call is now open.

Today, we launched a call for tenders to establish up to 7 AI Gigafactories across Europe, boosting Europe’s computing capacity and unlocking more than €30 billion in investment.

I am pleased to see Member States, industry, and the Commission coming together to build these facilities, which are key to strengthening our technological sovereignty.

This is a milestone for Europe in becoming an AI Continent.

link.europa.eu/qGDhv3


Questa voce è stata modificata (1 mese fa)